Wednesday, Sep 23, 2026
English News
  • Hyderabad
  • Telangana
  • AP News
  • India
  • World
  • Entertainment
  • Sport
  • Science and Tech
  • Business
  • Rewind
  • ...
    • NRI
    • View Point
    • cartoon
    • My Space
    • Education Today
    • Reviews
    • Property
    • Lifestyle
E-Paper
  • NRI
  • View Point
  • cartoon
  • My Space
  • Reviews
  • Education Today
  • Property
  • Lifestyle
Home | Science & Tech | Microsoft Admits To Signing Rootkit Malware In Supply Chain Fiasco

Microsoft admits to signing rootkit malware in supply-chain fiasco

According to Bleeping Computers, this driver, called "Netfilter," is a rootkit that was observed communicating with Chinese command-and-control (C2) IPs.

By IANS
Updated On - 28 June 2021, 03:17 PM
Microsoft admits to signing rootkit malware in supply-chain fiasco
whatsapp facebook twitter telegram

San Francisco: Tech giant Microsoft has now confirmed signing a malicious driver being distributed within gaming environments.

According to Bleeping Computers, this driver, called “Netfilter,” is a rootkit that was observed communicating with Chinese command-and-control (C2) IPs.


G Data malware analyst Karsten Hahn first took notice of this event last week and was joined by the wider infosec community in tracing and analysing the malicious drivers bearing the seal of Microsoft.

This incident has once again exposed threats to software supply-chain security, except this time it stemmed from a weakness in Microsoft’s code-signing process.

Microsoft said it is actively investigating this incident, although thus far, there is no evidence that stolen code-signing certificates were used.

The mishap seems to have resulted from the threat actor following Microsoft’s process to submit the malicious Netfilter drivers and managing to acquire the Microsoft-signed binary in a legitimate manner.

“Microsoft is investigating a malicious actor distributing malicious drivers within gaming environments,” the company was quoted as saying by the website.

“We have suspended the account and reviewed their submissions for additional signs of malware,” said Microsoft yesterday.

According to Microsoft, the threat actor has mainly targeted the gaming sector specifically in China with these malicious drivers and there is no indication of enterprise environments having been affected so far.

  • Follow Us :
  • Tags
  • gaming environments
  • malicious driver
  • Microsoft

Related News

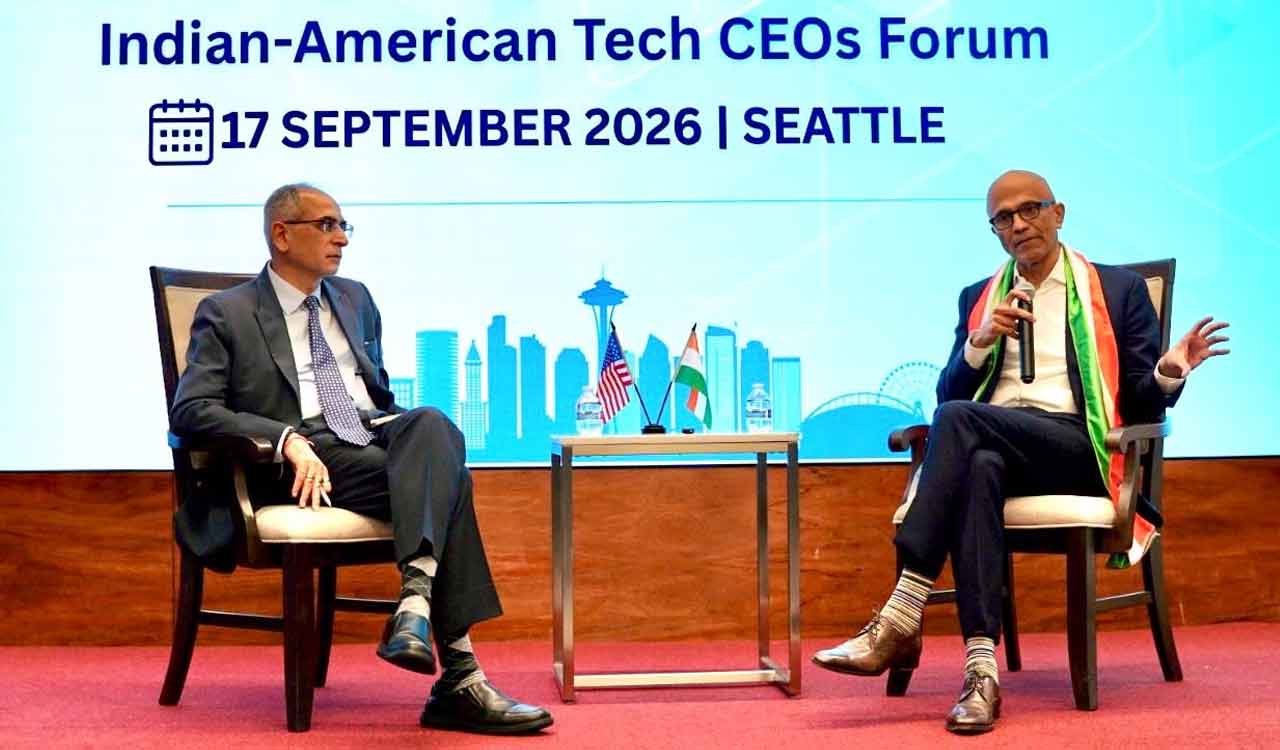
  • AI must stay under human control: Satya Nadella

    AI must stay under human control: Satya Nadella

  • Microsoft opens Hyderabad cloud region to boost India’s AI, cloud infra

    Microsoft opens Hyderabad cloud region to boost India’s AI, cloud infra

  • India emerges as major global hub for AI data centre investments

    India emerges as major global hub for AI data centre investments

  • Microsoft cuts Claude Code access as AI coding costs surge

    Microsoft cuts Claude Code access as AI coding costs surge

Latest News

  • US lawmakers propose AI safety framework, hotline with China

    28 minutes ago
  • Jurala right canal gets water amid farmers’ protests

    40 minutes ago
  • Nani seeks Telangana nod to watch The Paradise premiere with fans at RTC X Roads

    34 minutes ago
  • Japan raises UN Security Council reform with Guterres, spotlight on India’s G4 push

    48 minutes ago
  • Ram Pothineni wraps second schedule of directorial debut with night action sequence

    1 hour ago
  • Cartoon Today on Sept 23, 2026

    2 hours ago
  • India, Saudi Arabia discuss community welfare, consular issues in Jeddah

    9 hours ago
  • Man allegedly shoots wife, two priests dead in Azamgarh

    9 hours ago

company

  • Home
  • About Us
  • Contact Us
  • Privacy Policy

business

  • Subscribe

telangana today

  • Telangana
  • Hyderabad
  • Latest News
  • Entertainment
  • World
  • Andhra Pradesh
  • Science & Tech
  • Sport

follow us

  • Telangana Today Telangana Today
Telangana Today Telangana Today

© Copyrights 2024 TELANGANA PUBLICATIONS PVT. LTD. All rights reserved. Powered by Veegam

Telangana Today App